Skip to content

Align bank legal-name validation with Settings - #106807

Draft
MelvinBot wants to merge 1 commit into
mainfrom
claude-alignLegalNameValidation
Draft

MelvinBot wants to merge 1 commit into
mainfrom
claude-alignLegalNameValidation

Conversation

@MelvinBot

Copy link
Copy Markdown
Contributor

Explanation of Change

Align bank, wallet, beneficial-owner and signer legal-name character validation with the existing Settings legal-name rule, following the requested revision.

  • Replace every use of isValidLegalName with isValidDisplayName, without adding a configurable check.
  • Show the existing comma-or-semicolon error for prohibited separators. Preserve existing required-field, length and reserved-word checks.
  • Remove the obsolete validator and its Latin-only regex, and replace its tests with coverage for hyphens, apostrophes, non-Latin names, prohibited separators and required-field validation.

This fixes client-side character rejection; successful bank ownership verification is not claimed from automated browser testing.

Fixed Issues

$ #106743
PROPOSAL: #106743 (comment)

Tests

// TODO: The human co-author must fill out the tests you ran before marking this PR as "ready for review".
// Please describe what tests you performed that validates your change worked.

  • Verify that no errors appear in the JS console

Offline tests

// TODO: The human co-author must fill out offline verification before marking this PR as ready for review.

QA Steps

// TODO: The human co-author must fill out the QA tests you ran before marking this PR as "ready for review".
// Please describe what QA needs to do to validate your changes and what areas need regression testing.

  • Verify that no errors appear in the JS console

PR Author Checklist

  • I linked the correct issue in the ### Fixed Issues section above
  • I wrote clear testing steps that cover the changes made in this PR
    • I added steps for local testing in the Tests section
    • I added steps for the expected offline behavior in the Offline steps section
    • I added steps for Staging and/or Production testing in the QA steps section
    • I added steps to cover failure scenarios (i.e. verify an input displays the correct error message if the entered data is not correct)
    • I turned off my network connection and tested it while offline to ensure it matches the expected behavior (i.e. verify the default avatar icon is displayed if app is offline)
    • I tested this PR with a High Traffic account against the staging or production API to ensure there are no regressions (e.g. long loading states that impact usability).
  • I included screenshots or videos for tests on all platforms
  • I ran the tests on all platforms & verified they passed on:
    • Android: Native
    • Android: mWeb Chrome
    • iOS: Native
    • iOS: mWeb Safari
    • MacOS: Chrome / Safari
  • I verified there are no console errors (if there's a console error not related to the PR, report it or open an issue for it to be fixed)
  • I verified any copy / text that was added to the app is either coming verbatim from figma or has been approved by marketing (in order to get marketing approval, ask the Bug Zero team member to add the Waiting for copy label to the issue)
  • If a new code pattern is added I verified it was agreed to be used by multiple Expensify engineers
  • I tested other components that can be impacted by my changes (i.e. if the PR modifies a shared library or component like Avatar, I verified the components using Avatar are working as expected)
  • If new assets were added or existing ones were modified, I verified that:
    • The assets are optimized and compressed (for SVG files, run npm run compress-svg)
    • The assets load correctly across all supported platforms.
  • If the PR modifies code that runs when editing or sending messages, I tested and verified there is no unexpected behavior for all supported markdown - URLs, single line code, code blocks, quotes, headings, bold, strikethrough, and italic.
  • If the PR modifies a generic component, I tested and verified that those changes do not break usages of that component in the rest of the App (i.e. if a shared library or component like Avatar is modified, I verified that Avatar is working as expected in all cases)
  • If the PR modifies a component related to any of the existing Storybook stories, I tested and verified all stories for that component are still working as expected.
  • If the PR modifies a component or page that can be accessed by a direct deeplink, I verified that the code functions as expected when the deeplink is used - from a logged in and logged out account.
  • If the PR modifies the UI (e.g. new buttons, new UI components, changing the padding/spacing/sizing, moving components, etc) or modifies the form input styles:
    • I verified that all the inputs inside a form are aligned with each other.
    • I added Design label and/or tagged @Expensify/design so the design team can review the changes.
  • If the PR adds or modifies the UI:
    • I asked an AI agent to review the changes for accessibility issues and addressed its findings.
    • I tested with a screen reader (VoiceOver on macOS) and verified all new/changed elements are reachable with a logical focus order.
    • I verified all new/changed elements have meaningful accessible names and roles.
    • I verified state changes are announced (e.g. checked/unchecked, expanded/collapsed, selected).
  • I added unit tests for any new feature or bug fix in this PR to help automatically prevent regressions in this user flow.
  • If the main branch was merged into this PR after a review, I tested again and verified the outcome was still expected according to the Test steps.

AI Tests

  • Passed full Jest suite: npm test -- --silent --maxWorkers=4 — 2,372 suites passed, 1 skipped; 39,484 tests passed, 146 skipped; 160 snapshots passed. An earlier two-worker run timed out; the four-worker run completed successfully.
  • Passed targeted validation suite: 220 tests.
  • Passed npm run lint, npm run lint-changed, npm run typecheck, npm run spell-changed, npm run storybook -- --smoke-test --ci, and git diff --check.
  • Passed direct React Compiler checks for all three changed React components. The check-changed wrapper could not determine its base branch in this invocation, so the direct checks were used; changed-vs-base compiler comparison remains unverified.
  • The prescribed prettier npm script does not exist in this checkout. The repository's pre-commit oxfmt hook passed on all six changed files.
  • Staged code review returned no violations.
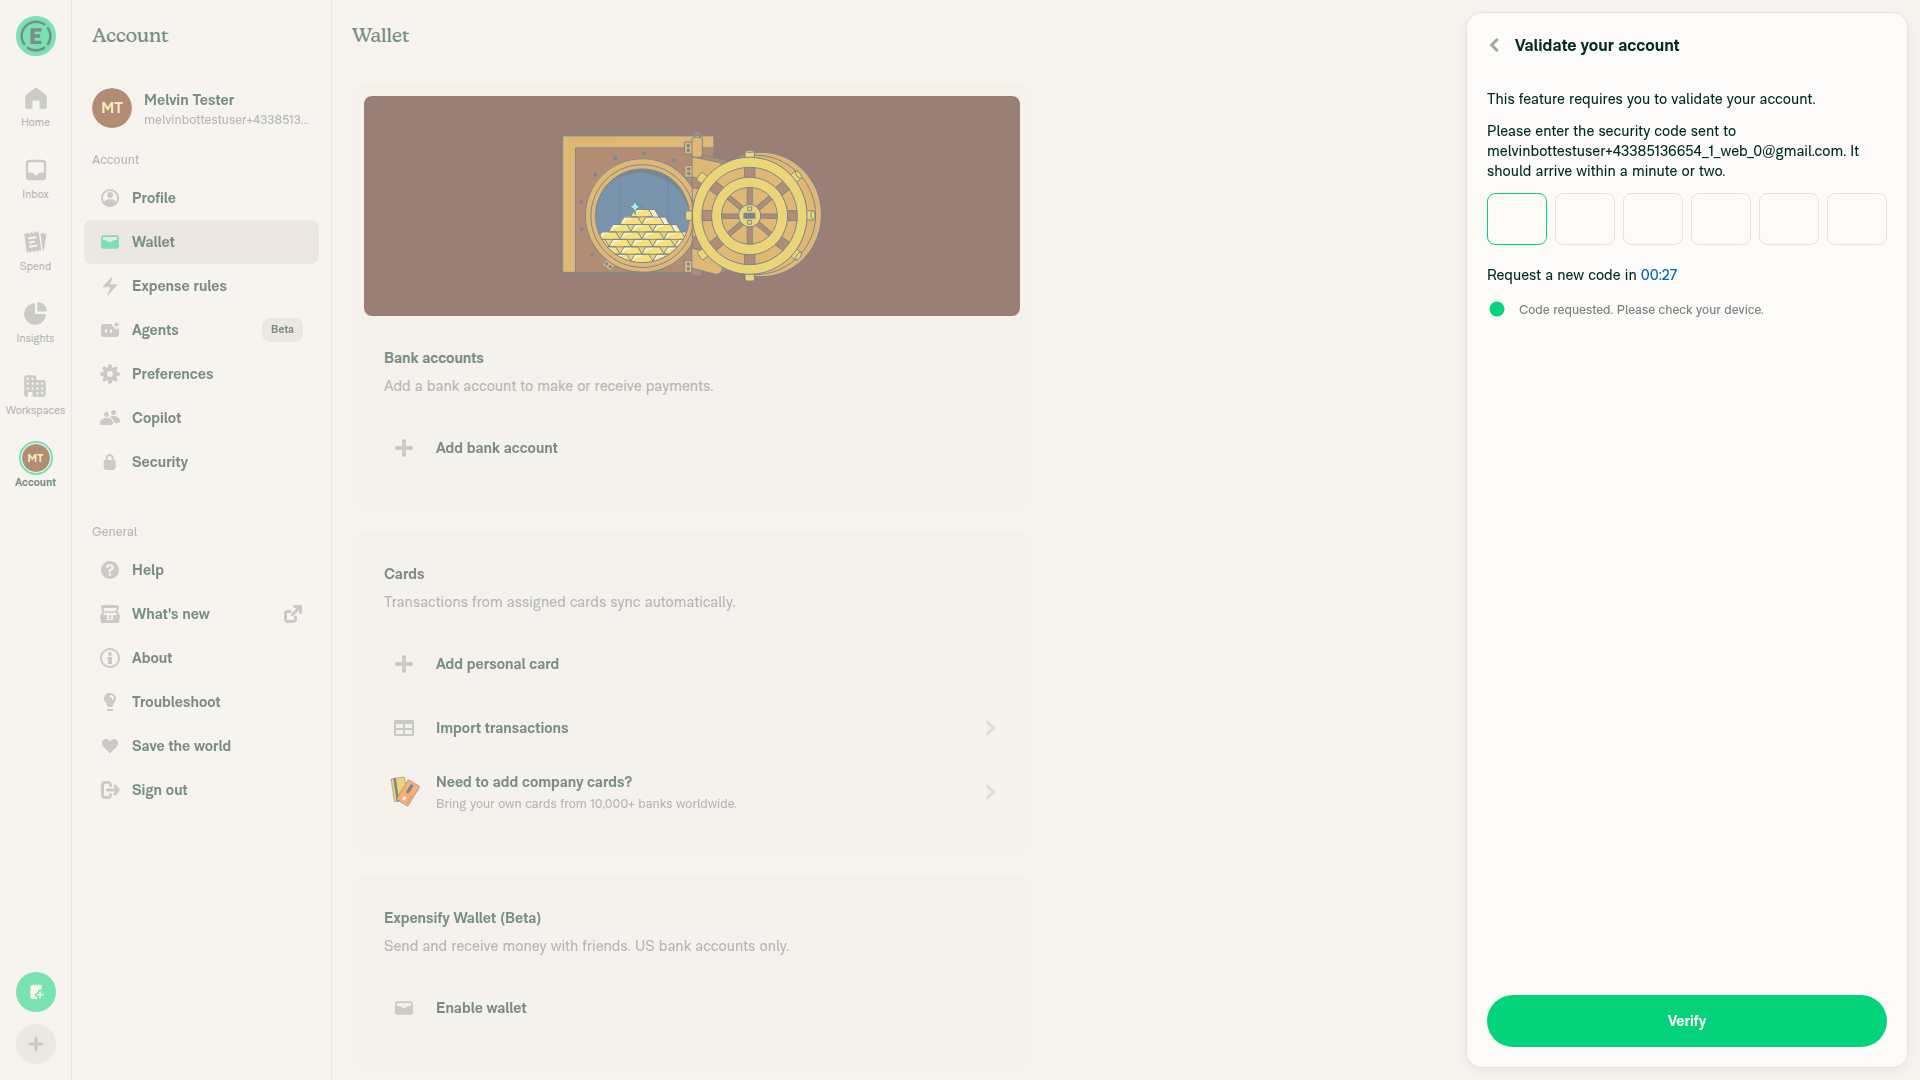
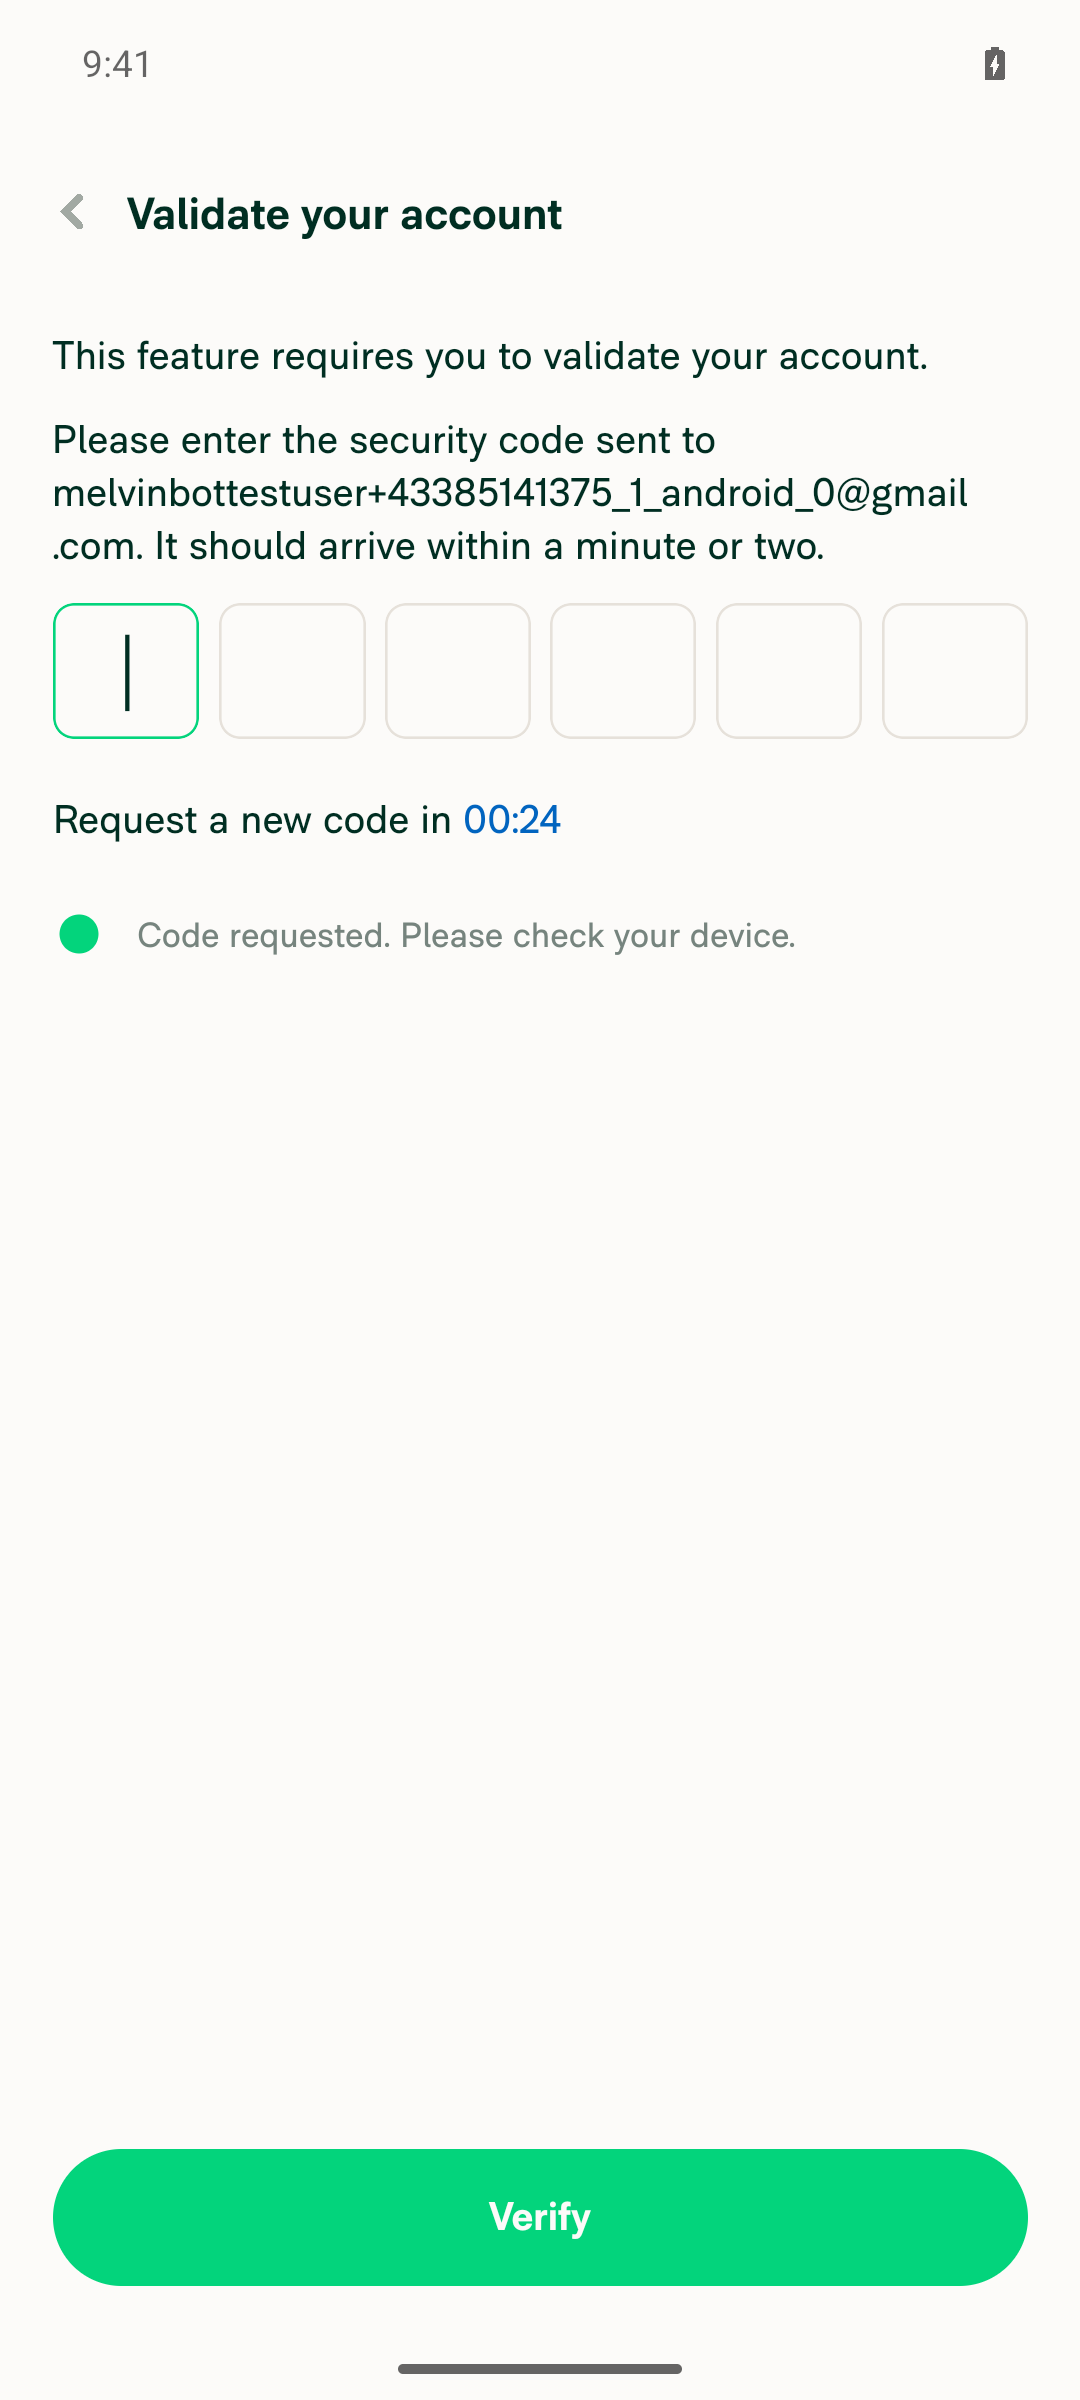
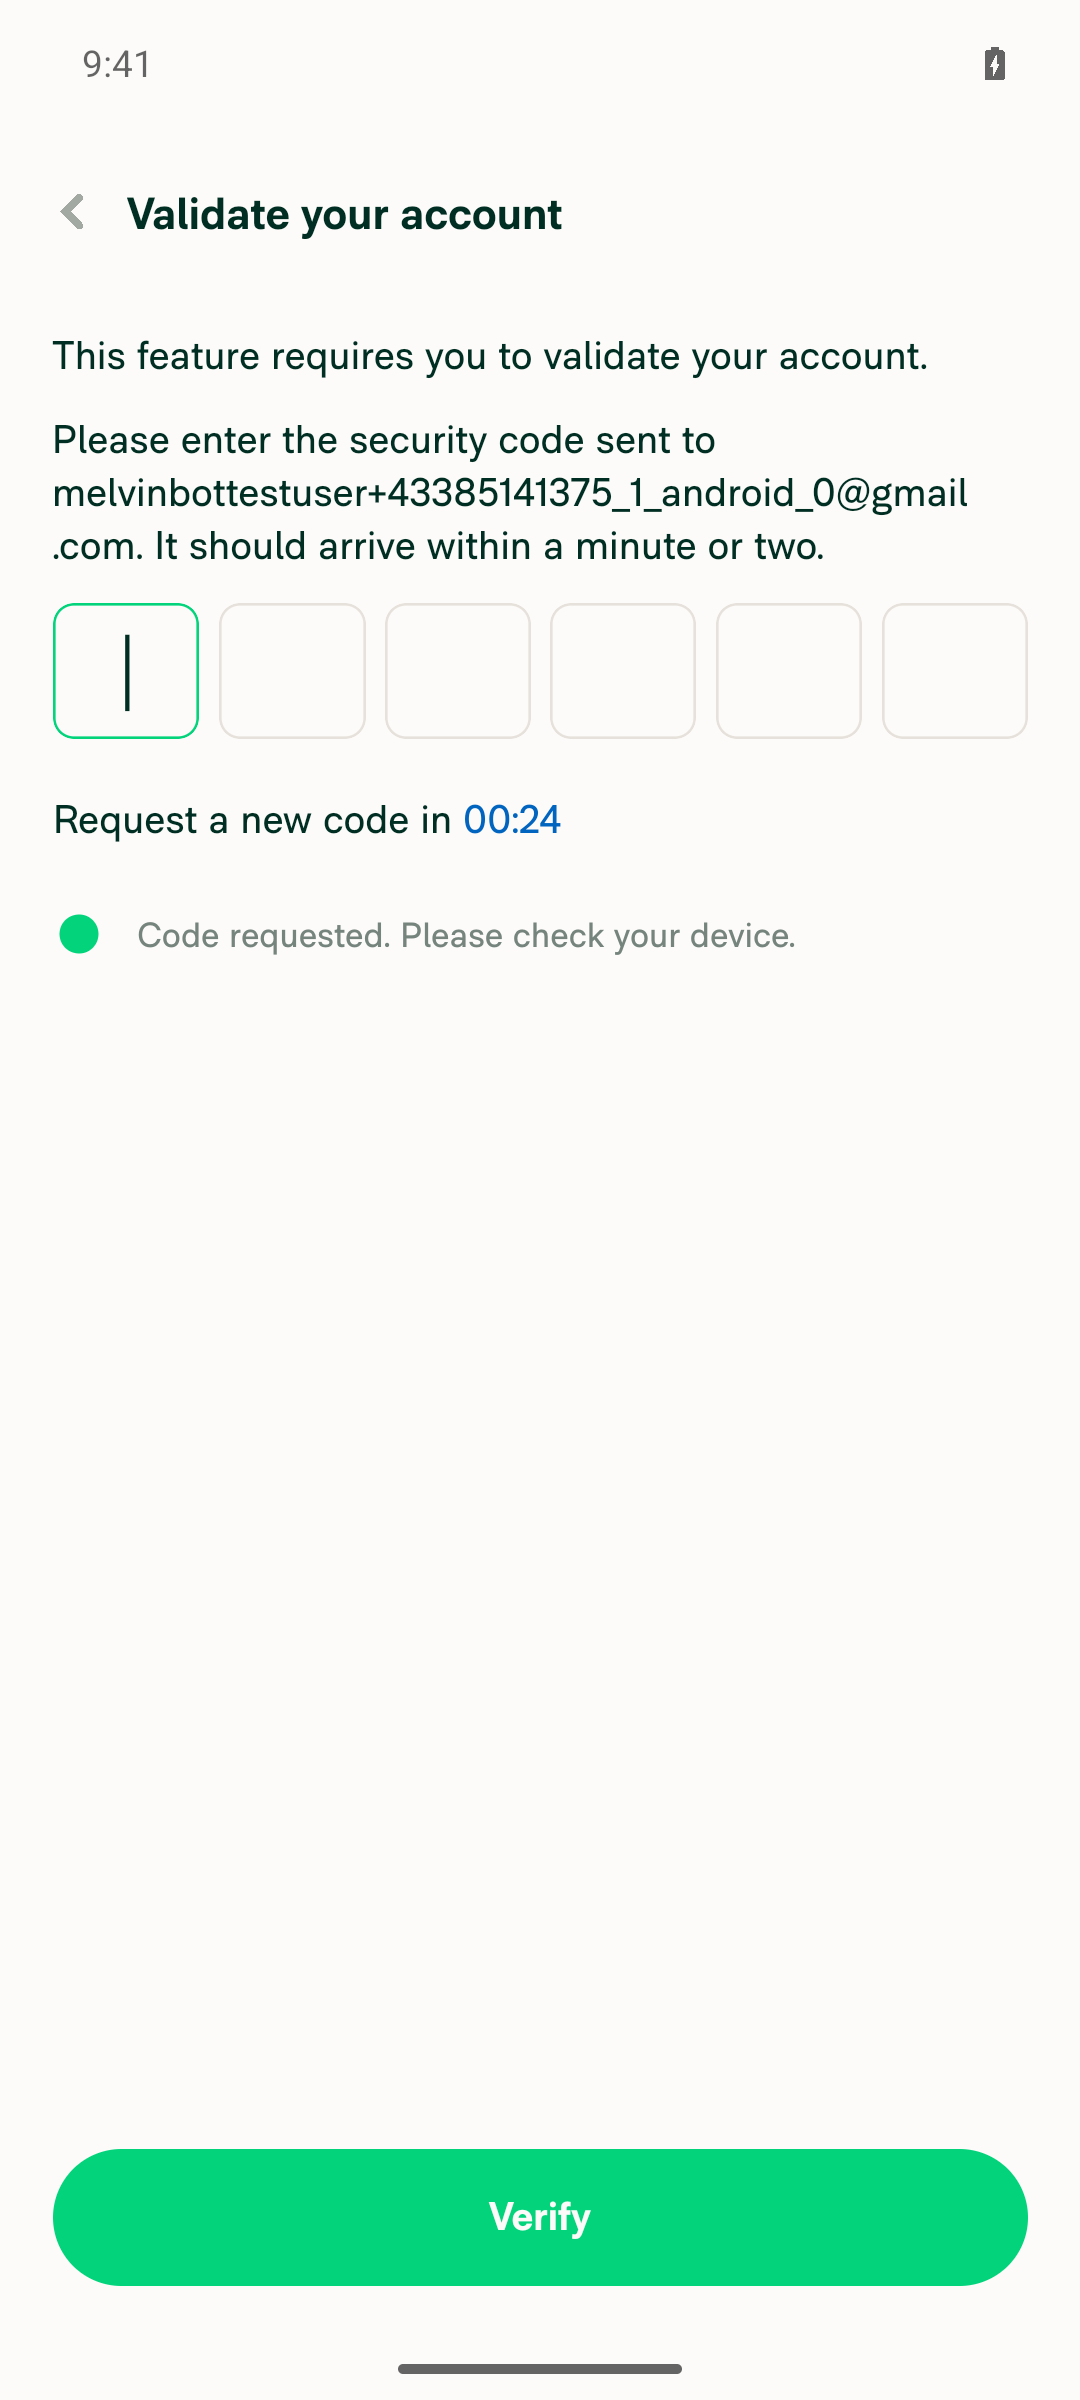
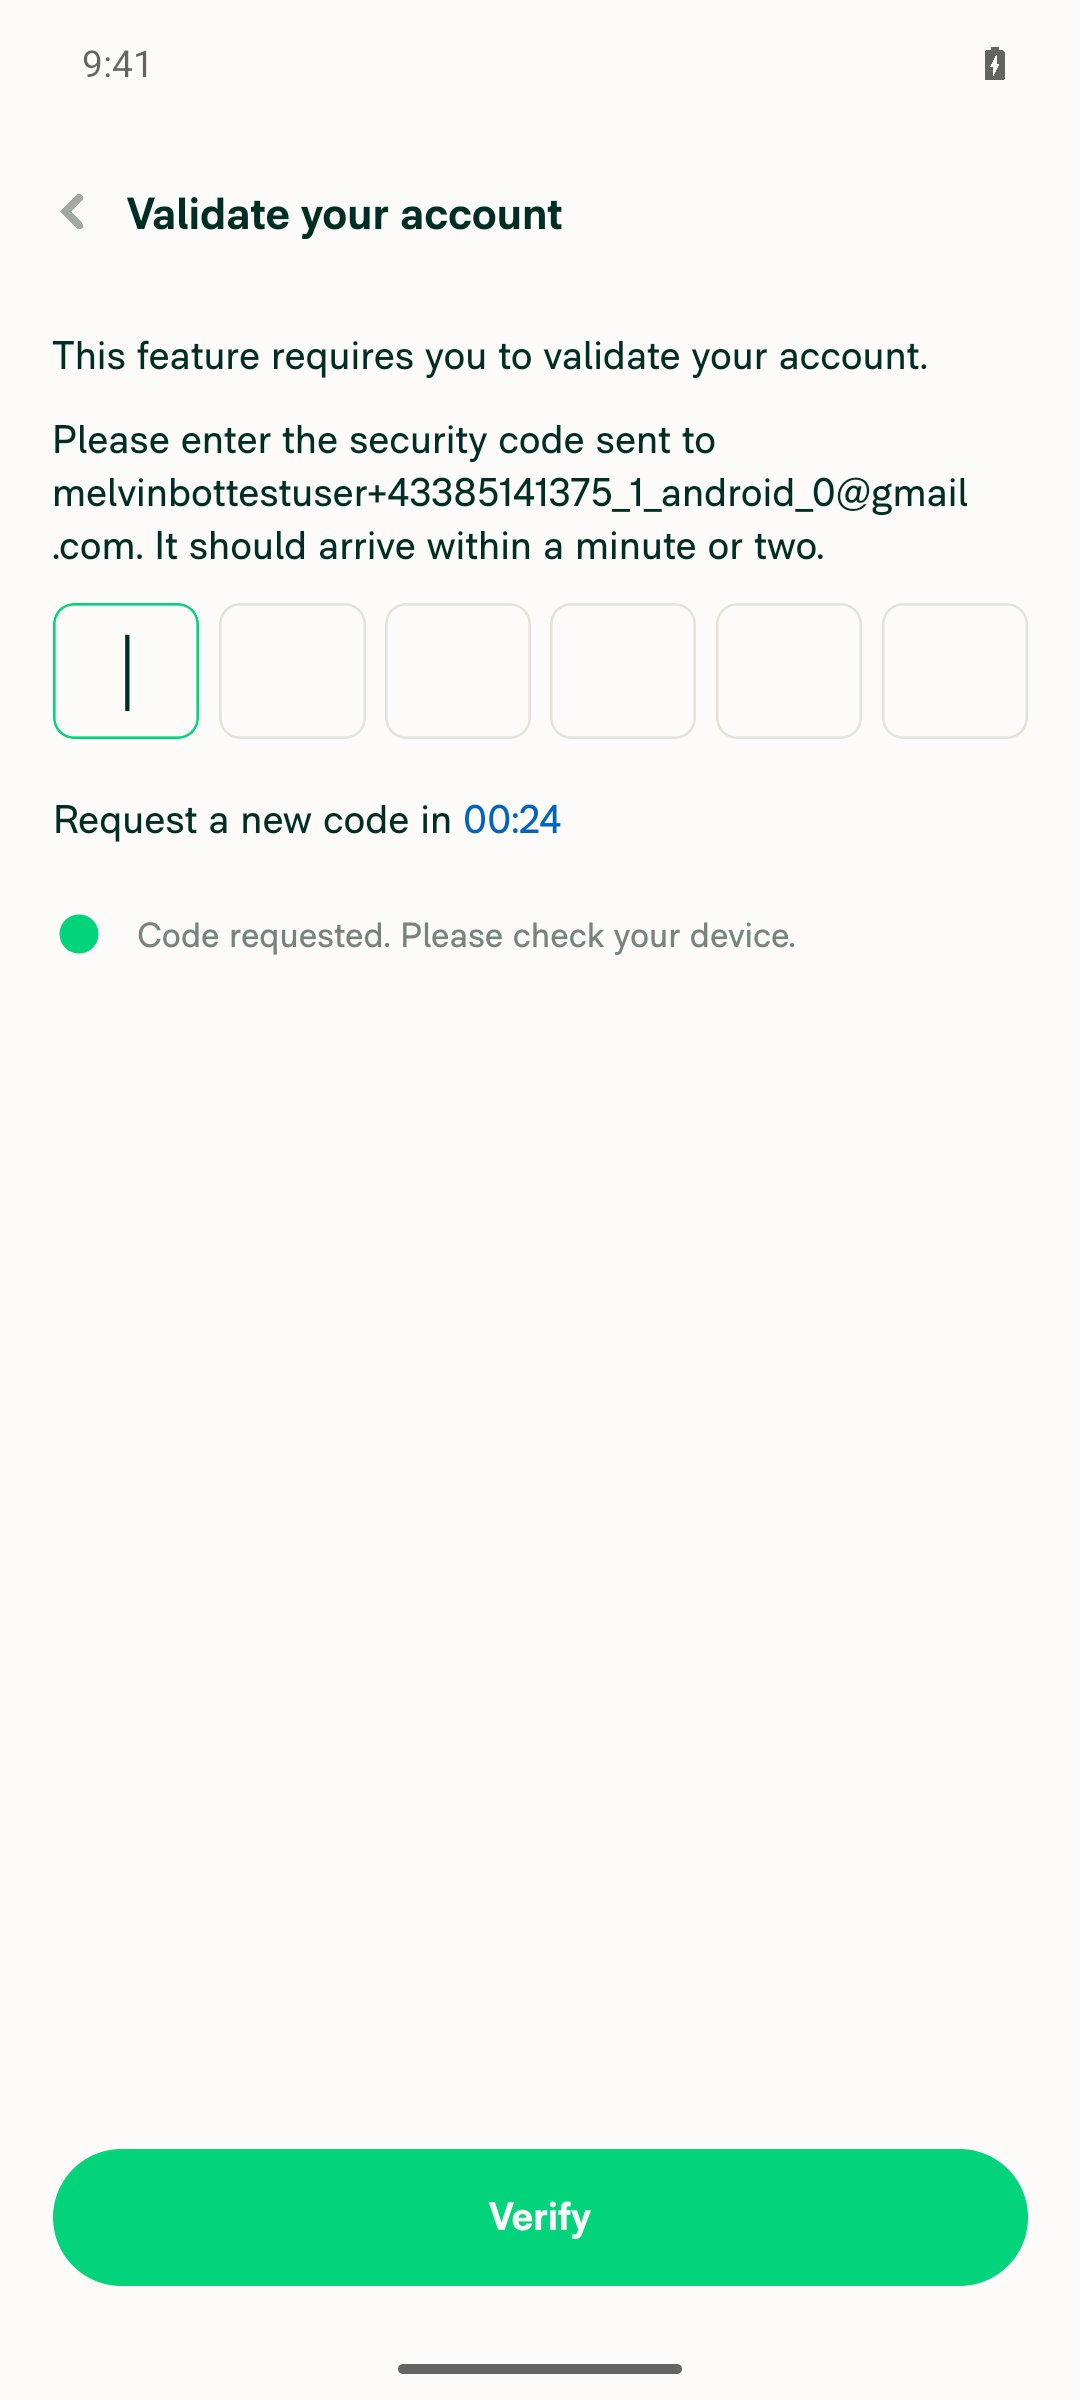
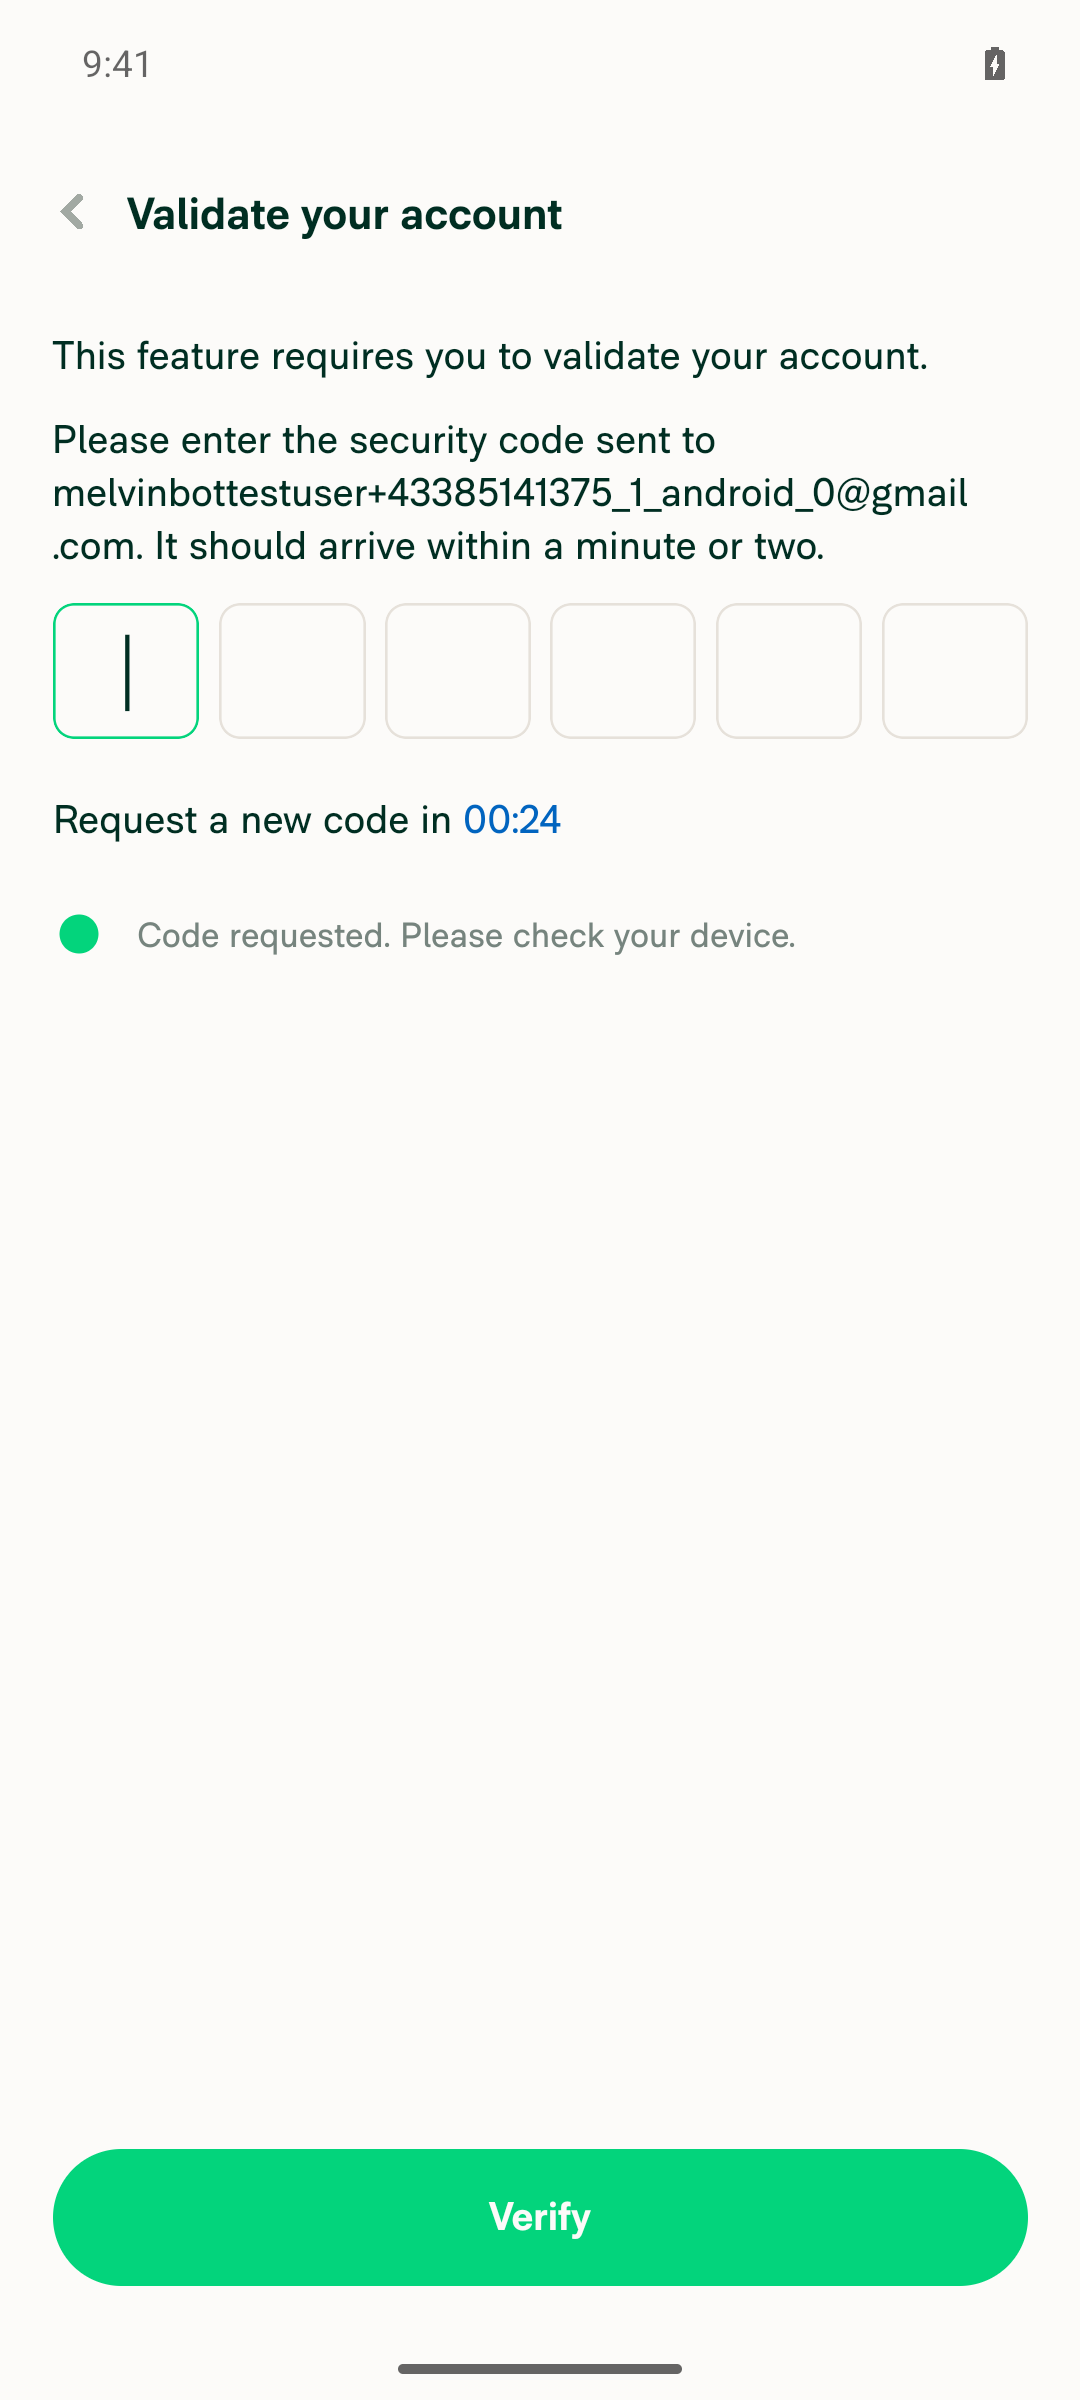
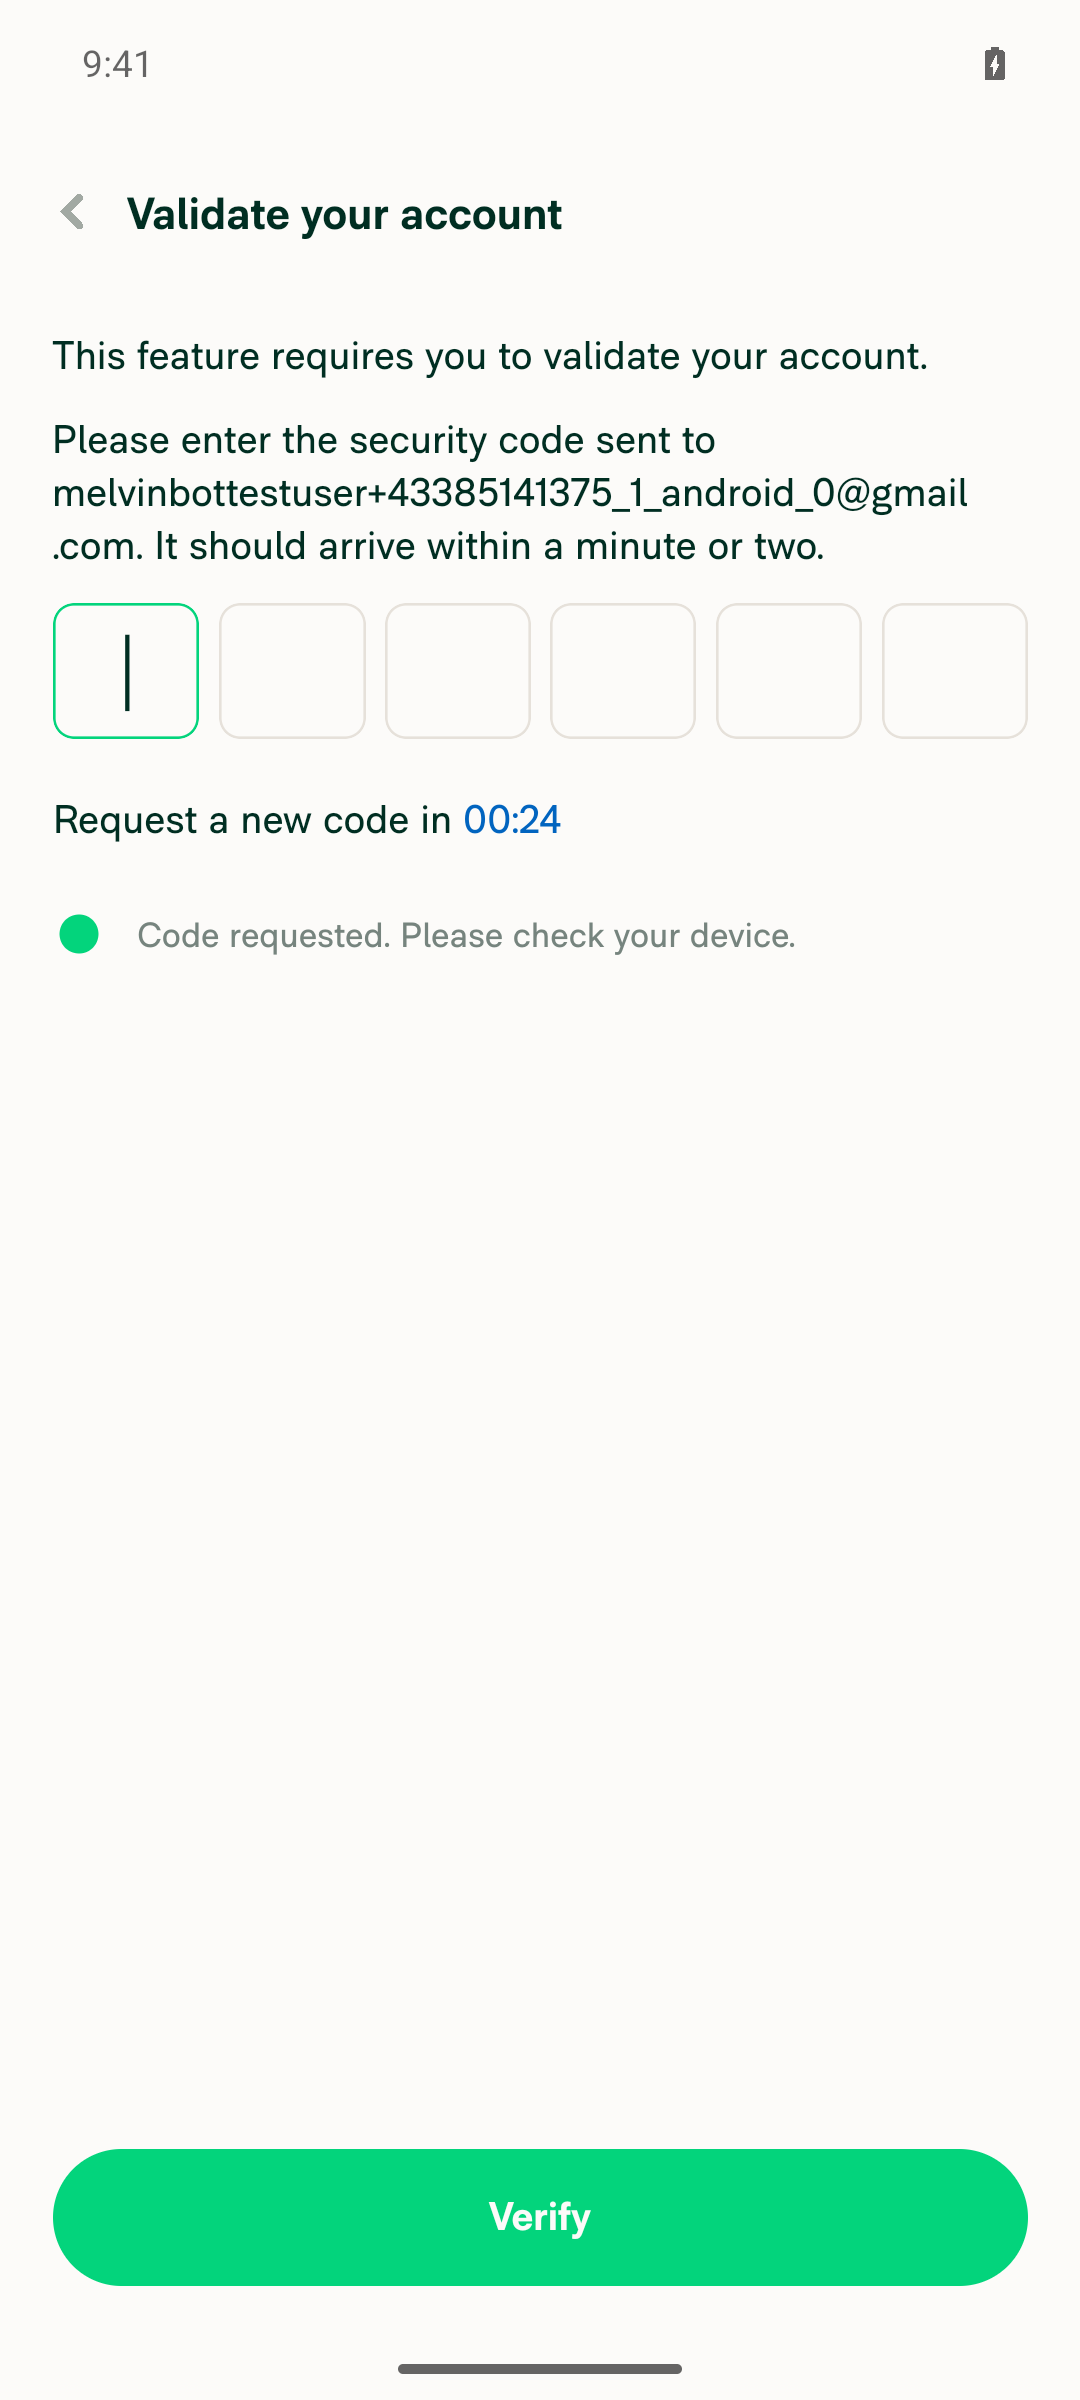
  • Browser verification was blocked by an emailed security-code gate before legal-name entry. Neither the shared name form nor signer-name flows were verified interactively. No real bank was linked and no sensitive verification was submitted.

Security-code gate before wallet name entry

Contributor branch access

This draft uses an upstream branch because a contributor fork was not available. To copy it to your own fork:

git remote add upstream https://github.com/Expensify/App.git
git fetch upstream claude-alignLegalNameValidation
git checkout -b claude-alignLegalNameValidation upstream/claude-alignLegalNameValidation
git push -u origin claude-alignLegalNameValidation

You can then close this draft and open a replacement from your fork.

Screenshots/Videos

Android: Native
Android: mWeb Chrome
iOS: Native
iOS: mWeb Safari
MacOS: Chrome / Safari

Co-authored-by: Linh Vo <linhvovan29546@users.noreply.github.com>
@MelvinBot

MelvinBot commented Nov 13, 2026 •

Copy link
Copy Markdown
Contributor Author

🤖 Web test steps verification results: ⚠️ partial

Verified the existing signed-in session on dev NewDot web. Adding a bank account required an emailed security code, blocking bank selection and name-validation testing; no bank credentials or sensitive verification data were submitted.

Security-code gate after adding a bank account

Step Status
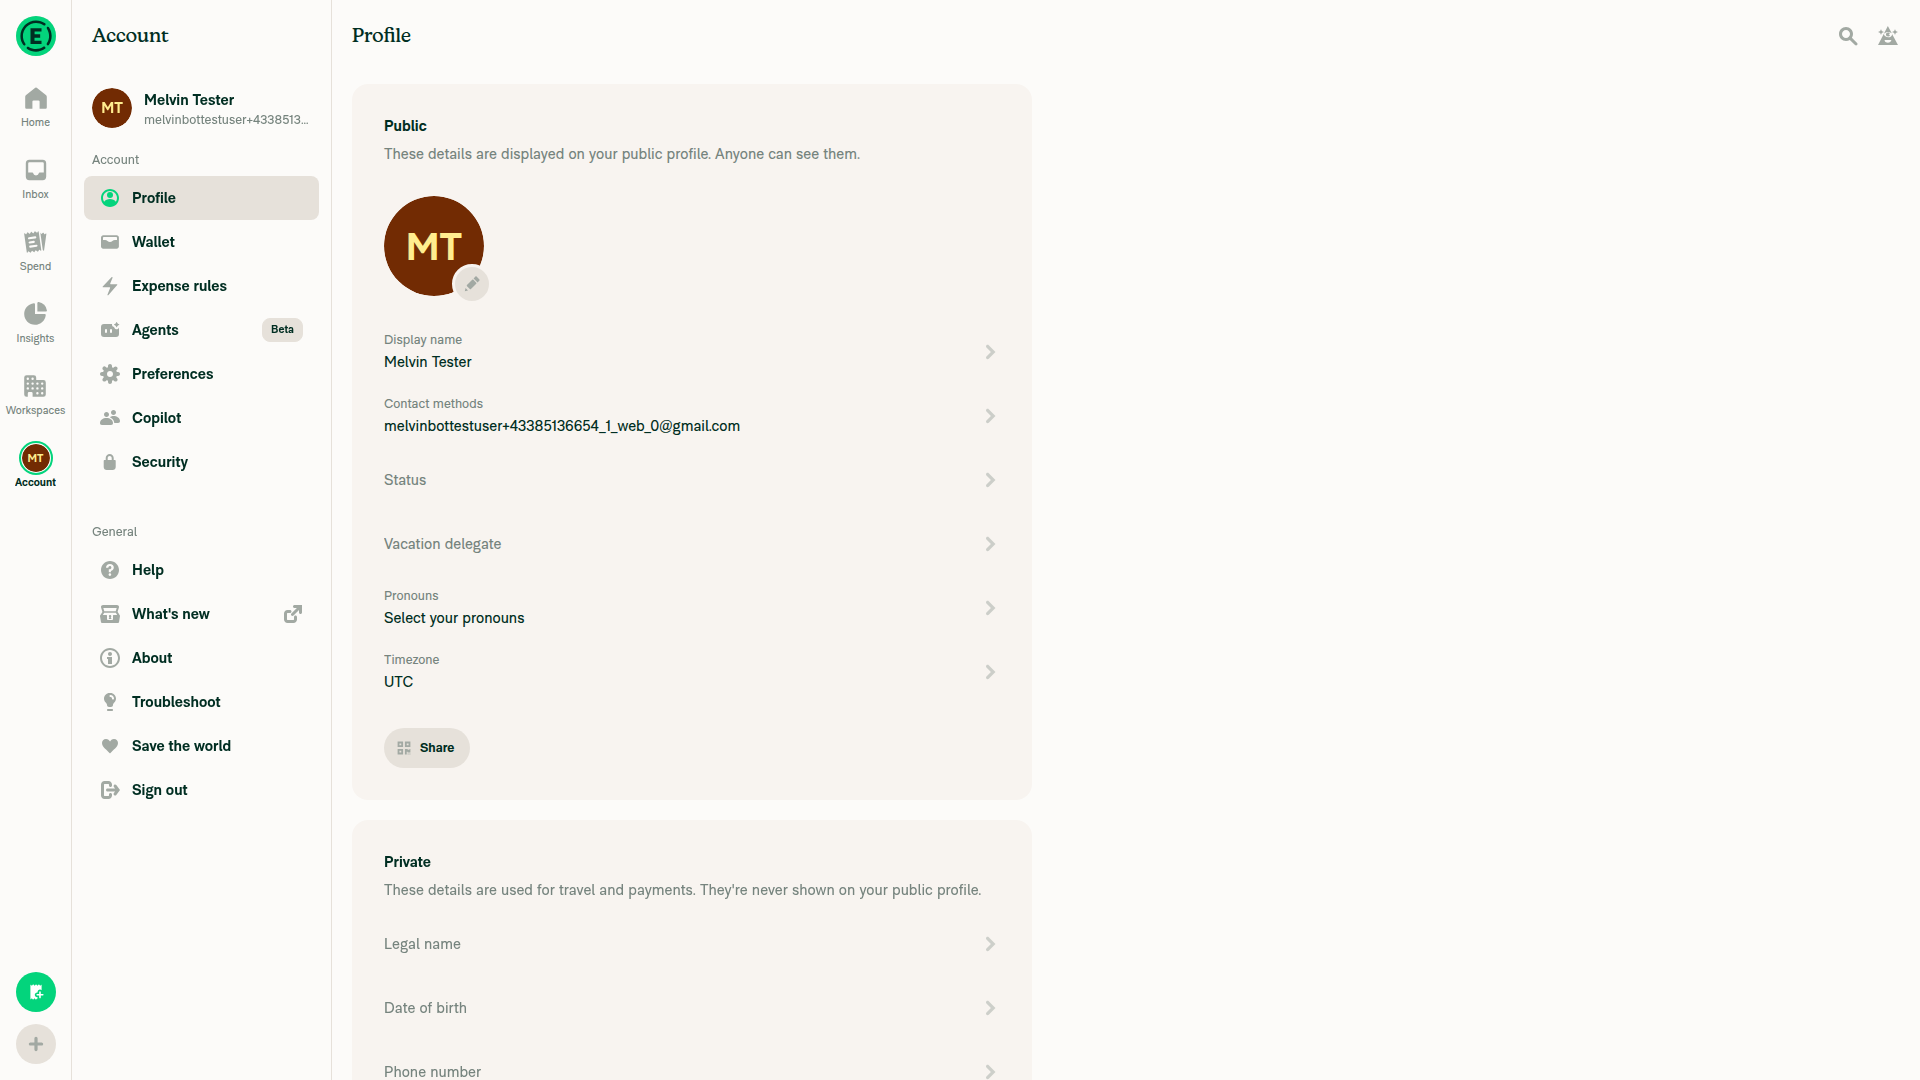
1. Log in using the existing sessionConfirmed authenticated Profile and Wallet were accessible.
Authenticated Account Profile
✅
2. Attempt Bank of America connectionClicked Add bank account. An emailed security-code gate blocked progress before bank selection.
Security-code gate after adding a bank account
❌
3. Connect through PlaidBlocked before Plaid; no bank credentials submitted.
❌
4. Reach ownership-verification legal-name stepNot reached because of the security-code gate.
❌
5. Enter and read back a hyphenated legal nameNo legal-name field in the requested flow was reached.
❌
6. Accept hyphenated names without the Latin-character errorNeither client-side acceptance nor successful ownership verification could be established.
❌
7. Verify no JavaScript console errorsUnverified: supported testing tools did not expose console-error read-back.
❌
Additional: Accept apostrophes and non-Latin namesBlocked before name entry.
❌
Additional: Reject commas and semicolonsBlocked before name entry.
❌
Additional: Reject empty required namesBlocked before name entry.
❌
Additional: Accept hyphens in signer formsSigner forms were not reached. These blocked checks are not confirmed regressions.
❌

view run · view recording

@codecov

codecov Bot commented Nov 13, 2026 •

Copy link
Copy Markdown

Codecov Report

❌ Looks like you've decreased code coverage for some files. Please write tests to increase, or at least maintain, the existing level of code coverage. See our documentation here for how to interpret this table.

Files with missing lines Coverage Δ
src/CONST/index.ts 96.09% <ø> (ø)
src/libs/ValidationUtils.ts 66.76% <ø> (-0.20%) ⬇️
src/components/SubStepForms/FullNameStep.tsx 0.00% <0.00%> (ø)
...bursementAccount/EnterSignerInfo/subSteps/Name.tsx 0.00% <0.00%> (ø)
...rsementAccount/NonUSD/SignerInfo/subSteps/Name.tsx 0.00% <0.00%> (ø)
... and 6 files with indirect coverage changes

@MelvinBot

MelvinBot commented Nov 13, 2026 •

Copy link
Copy Markdown
Contributor Author

🤖 Android test steps verification results: ⚠️ partial

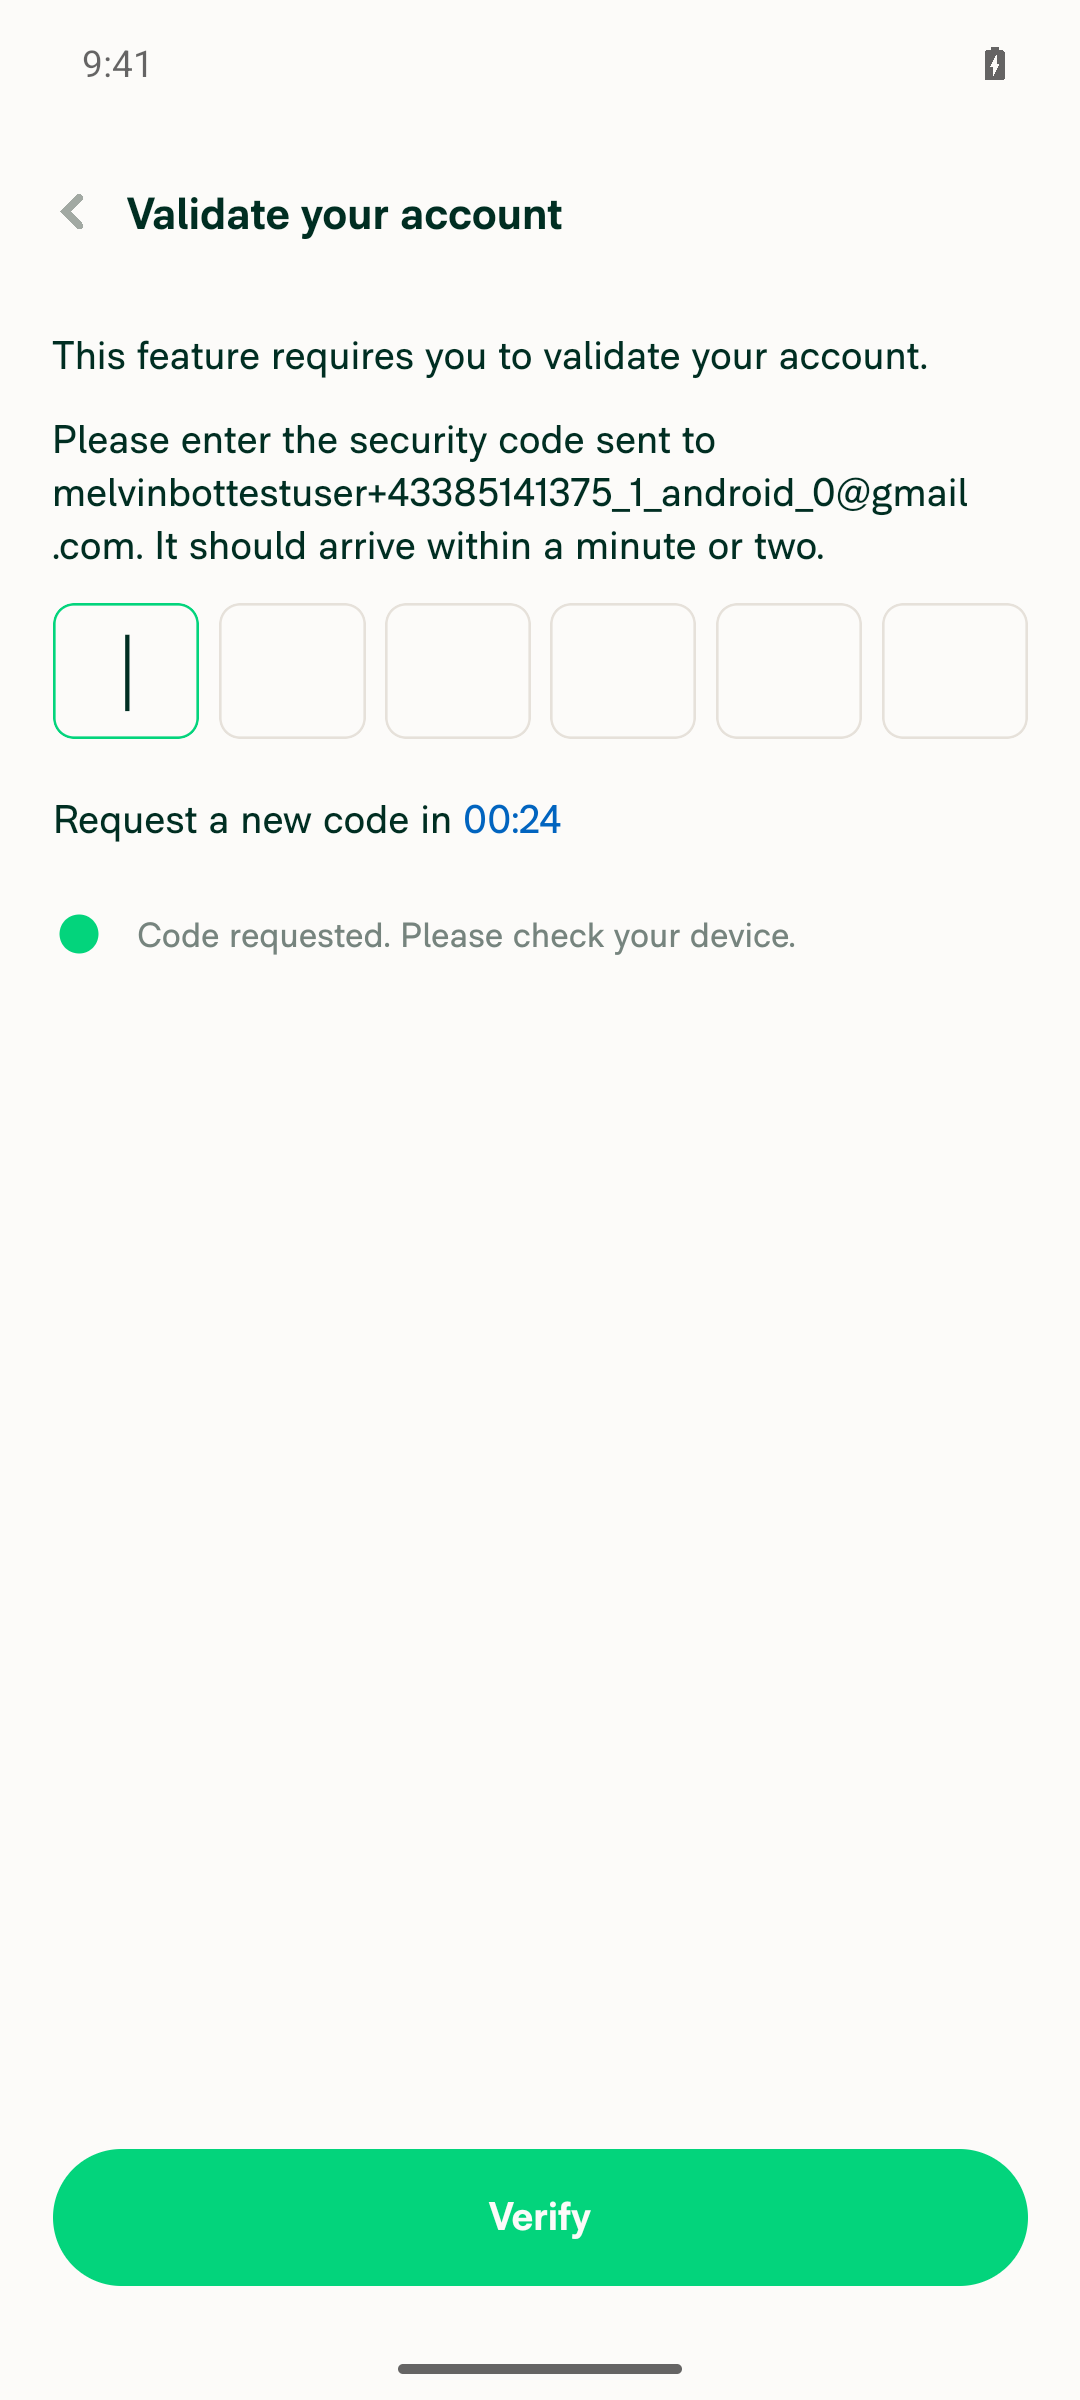
Verified on standalone Android NewDot. Adding a bank account reached an emailed security-code gate, so testing stopped without submitting credentials or verification data; hyphen acceptance remains unverified, not a confirmed regression.

Final UI without a visible JS error overlay

Step Status
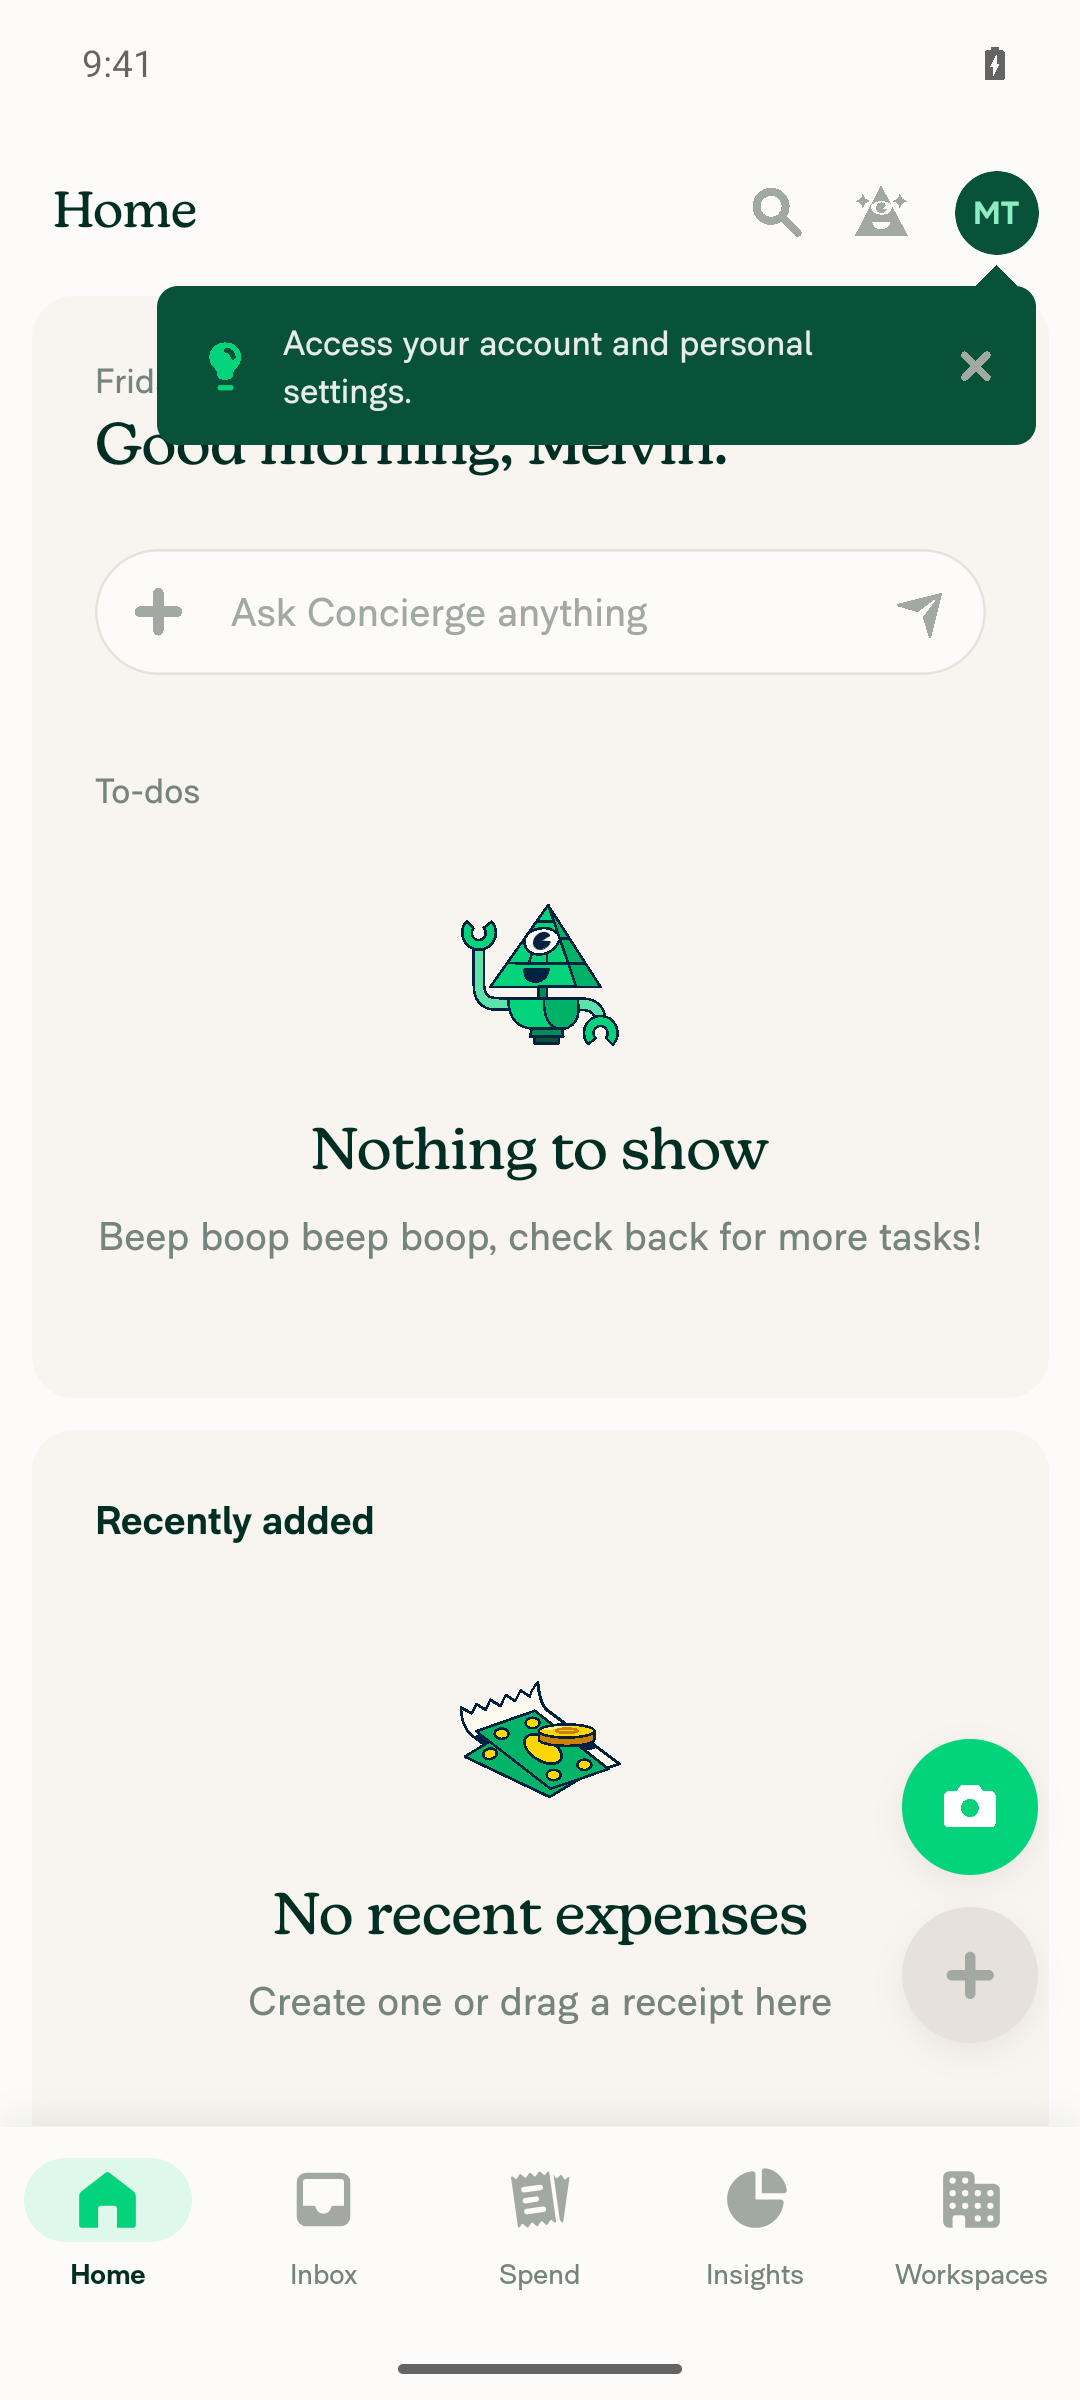
1. Use existing signed-in sessionConfirmed signed in with onboarding complete; authenticated Home and Wallet were accessible.
Authenticated Android NewDot Home
✅
2. Attempt Bank of America connectionWallet → Add bank account required an emailed security code before bank selection.
Account validation blocks bank selection
❌
3. Connect through Plaid using safe fixturesBlocked before Plaid. No bank fixture was available; no credentials or security codes were submitted.
Security-code prerequisite blocks Plaid
❌
4. Reach ownership-verification legal-name stepNot reached because of the security-code prerequisite.
Gate preceding ownership verification
❌
5. Enter and read back a hyphenated legal nameNot executed: the legal-name field was inaccessible.
Blocker preventing legal-name entry
❌
6. Accept hyphens without the Latin-character errorNeither client-side acceptance nor successful ownership verification was tested.
Blocker preventing hyphen-validation testing
❌
7. Verify no JavaScript console errorsUnverified: console inspection was unavailable under tester permissions. No visible error overlay appeared, which does not prove a clean console.
Final UI without a visible JS error overlay
❌

view run · view recording

This branch has not been deployed

No deployments
Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

Melvin-Test-Android Melvin-Test-Web Triggers Melvin to run the testing steps of the PR on web

Projects

None yet

Development

Successfully merging this pull request may close these issues.

2 participants